Explorar las categorías
Explora
Fiverr Pro
Español
$
USD
Robotics and Embedded Systems Engineer
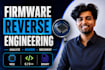
Need to understand embedded firmware without the original source code?
I perform authorized reverse engineering and binary analysis of firmware, embedded software and protocols.
I can analyze BIN, HEX and ELF files to:
Methods can include Ghidra, disassembly, decompilation, static analysis, debugging and binary comparison.
Deliverables can include architecture notes, function analysis, protocols, diagrams and feasibility results plus a structured report.
I only analyze software, firmware and devices you own or are authorized to analyze.
Send the firmware/files, device information, platform details and your goal before ordering so I can scope feasibility.


Should I contact you before ordering?
Yes, especially for large or unusual projects. Send a brief description of the system, available files, platform/MCU information and what you want to understand. I can then recommend the appropriate package.
What types of firmware can you analyze?
I can analyze Embedded C, C, C++, Assembly, firmware source code, project files, and suitable binary/firmware files depending on the project and available information.
Can you analyze STM32, ESP32, Arduino and Raspberry Pi projects?
Yes. I can work with firmware and software-based projects involving STM32, ESP32, Arduino, Raspberry Pi and other supported embedded platforms.
Can you analyze robotics control systems?
Yes. I can analyze motor-control logic, sensor processing, control flow, subsystem dependencies, communication and software-based robotics architectures.
Can you reverse engineer firmware?
Yes, for legitimate analysis and documentation. You must have the legal right to provide the files. I do not bypass DRM, authentication, signing, licensing or anti-tamper protections.
Do you work with binary firmware files?
Yes, where static analysis is technically feasible. The depth of analysis depends on the file format, available symbols, architecture and information provided.
Do you work with physical hardware?
No. This Gig focuses on file and software-based analysis. I do not perform soldering, board repair, oscilloscope testing, bench testing or physical hardware debugging.
What will I receive after the analysis?
Depending on your package, you can receive architecture analysis, module mapping, peripheral information, protocol analysis, control/data-flow documentation, risks, feasibility findings and a PDF/DOCX report.
Can you analyze communication protocols?
Yes. Where the required information is available, I can analyze interfaces such as UART, SPI, I2C, CAN and other software-implemented communication protocols.
Can you compare two firmware versions?
Yes. I can compare provided firmware/source files to identify relevant structural, functional and code-level differences where technically possible.