Explorar las categorías
Español
$
USD
Conecta tu IA a Fiverr
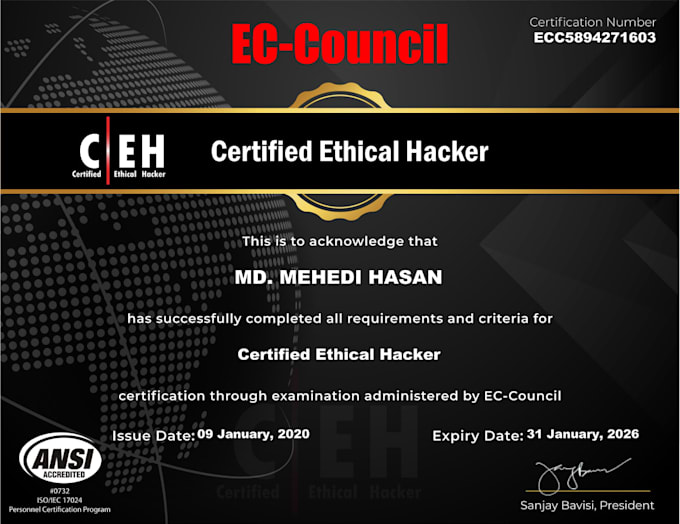
Security Consultant at Big Four, Penetration Tester, 6 CVEs
Nivel 2
Ha cumplido con los criterios de alto rendimiento y tiene un historial comprobado de cumplimiento de las expectativas de los clientes.
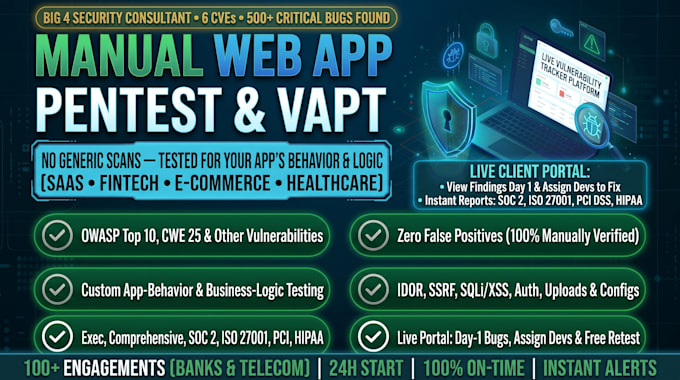
Is your web app secure, or just not hacked yet? I deliver manual penetration testing (VAPT) for SaaS, startups and businesses, not scanner-generated reports.
WHAT YOU GET
WHY ME
Big Four cybersecurity consultant with banking and telecom experience. 500+ critical vulnerabilities across 100+ apps, six published CVEs and 100% on-time delivery.
HOW IT WORKS
Not sure which package fits? Message me.


_grybq1.jpg)

Aplicación de prueba:
Sitio web
Dispositivo:
PC
•
Mac
•
Linux
•
iPhone
•
Teléfono móvil Android
Do you need my source code or credentials?
No source code for a black-box test. For Standard and Premium, create one test account per role you want tested. Credentials are shared only on the order page and deleted after delivery. NDA on request.
Is this an automated scan or a manual test?
Both, but the value is manual. Tools cover the basics; most of my time goes into authentication, access control and business logic by hand, and every finding is verified before it enters the report.
What does the report contain?
Executive summary, scope and methodology, a findings table by CVSS severity, and for each finding: description, impact, reproduction steps with screenshots or requests, and a specific fix. White-label available.
Can I see a sample report?
Yes. A redacted sample is attached to this gig as a PDF. Message me if you want a sample for a specific technology.
Will testing affect my live site?
Testing is non-destructive: no denial of service, no data deletion, no spam to real users. I recommend a staging environment when available; on production I keep automated scanning light.
Do you retest after we fix the issues?
Standard and Premium include one retest of all findings within 30 days of delivery, with an updated report you can share with customers or auditors. Basic can add a retest as an extra.
What is the difference between a vulnerability assessment and a penetration test?
A vulnerability assessment finds and lists weaknesses, mostly with tools. A penetration test proves which ones an attacker can actually exploit and how far they get. You get both here: every finding is verified and exploited safely, then ranked.
Can you test a site I do not own?
Only with written authorization from the owner, confirmed in the order requirements. Without it the order is cancelled, no exceptions.
Why are you more expensive than the US$20 gigs?
Those gigs deliver a scanner export. This test is done by a consultant who tests banks and telecom operators for a living, and the report is the same standard those clients receive.
What is Vexil (Client Portal)?
Vexil is my private client website. With Standard or Premium you get a login: each vulnerability I confirm appears there the same day with proof and a fix, your developer marks it fixed and asks me to retest, and you download the report as PDF, Word or Excel. The PDF is also delivered here.