Explorar las categorías
Español
$
USD
Conecta tu IA a Fiverr

Cybersecurity Analyst
Habilidades
Revisa mis servicios
Application Security Analyst
BCP • Tiempo completo
Jul 2026 - Present • 4 mos
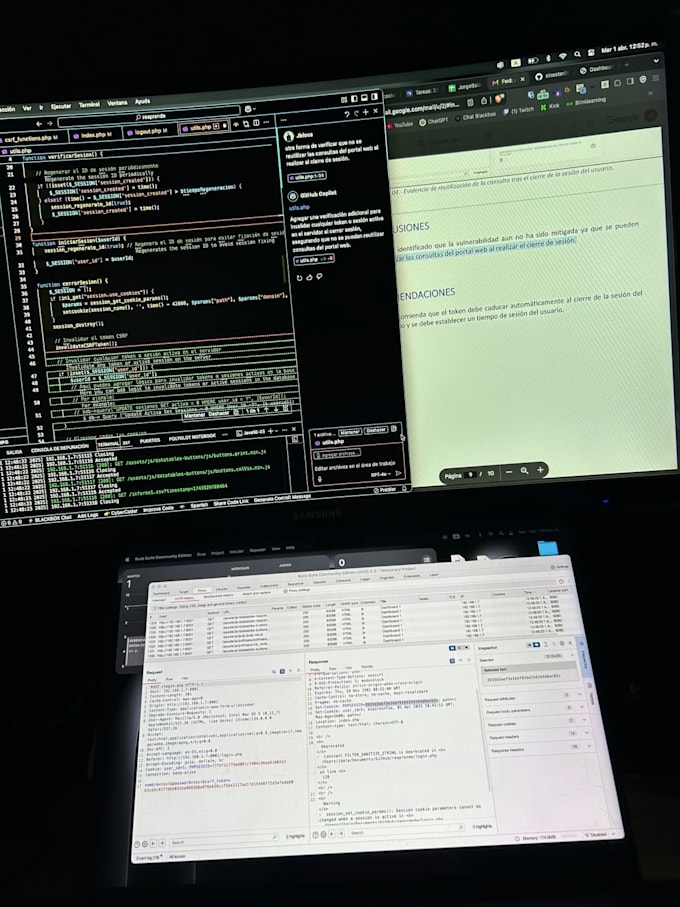
Application Security Analyst at one of Latin America's largest banks (via Clarity Services SAC). - Assessed the maturity of security practices across the application development lifecycle, identifying and correcting violations of industry standards (NIST, PCI DSS, ISO 27001). - Helped define the scope of security testing and ethical hacking engagements, delivering vulnerability analyses used as input to the bank's risk assessment process. - Ran periodic security reviews, identifying gaps and feeding them into the bank's risk management plan, with findings documented in internal repositories.
Senior Software Engineer & Security Lead
INTERCERT INC • Tiempo completo
Jul 2025 - Oct 2026 • 1 yr 3 mos
Led the security and cloud architecture of an e-learning platform. - Designed and built a 3-tier operational SOC (Macro/Meso/Micro) with Grafana: real-time GeoIP threat map, hour-by-day attack heatmap, offensive tool fingerprinting (SQLMap, Python scripts, headless browsers) and payment tampering detection before requests reach the payment processor. - Developed a custom Django AppSec middleware that detects SQLi and XSS at the application layer, before the ORM, integrated with Cloudflare Threat Intelligence for IP reputation. - Built a DevSecOps pipeline in GitHub Actions with JWT security analysis, payment flow checks and static code review on every pull request. - Implemented rate limiting and throttling on the REST API, eliminating critical brute-force and mass-scraping vulnerabilities found in an internal audit. - Led the AWS architecture (EC2, S3, Amplify): 40% faster API response times and 35% lower transfer costs using Cloudflare R2. - Set the stack's security standards: Linux hardening, encrypted secrets management and RBAC. Zero documented security incidents since implementation.
