Explorar las categorías
Explora
Fiverr Pro
Español
$
USD

Node.js and Express API security hardening: security headers, rate limiting, CORS, and an OWASP ZAP vulnerability scan before and after.
Most Node apps ship with no security headers, no rate limits and wide-open CORS. None of that shows until someone brute-forces your login or scrapes your API dry. I close those gaps and prove it with a scan.
WHAT I DO
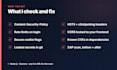
- Security headers with helmet: CSP, HSTS, frame and sniffing protection
- A Content-Security-Policy that does not break your app
- Rate limiting, stricter on login and signup
- CORS locked to your real frontend
- Cookie flags: HttpOnly, Secure, SameSite
- Dependency audit for known CVEs
- OWASP ZAP baseline scan of your live site
WHAT YOU GET
- Fixes committed to your repo
- A plain-English report of what was exposed and what changed
PORTFOLIO: GameVerse's Express API runs helmet with a custom CSP, global and login-specific rate limits, and a ZAP scan on every deploy.
Send me your URL. I will tell you what I see before you order.
Recuerda que incluir temas, plantillas o cualquier otro elemento que viole los derechos de terceros o las leyes aplicables en los trabajos entregados va en contra de las políticas de Fiverr. Puedes ver más información en Guía para la creación digital responsable.
Reliable Web Development and Cybersecurity Support for Your Projects
Idiomas
Is this a penetration test?
No. It is automated scanning plus hardening of the common gaps. A real pentest is manual and costs far more, and I will not dress this up as one.
Will a CSP break my site?
A careless one will. I start in report-only mode, fix what it flags, then enforce it, so nothing breaks in production.
My app is not Express. Can you still help?.
The Basic scan works on any website. The fixes are for Node and Express. For Django, FastAPI or Next.js, message me first.
Can you also put Cloudflare in front of it?
Yes. Add the Cloudflare WAF extra: I set up the WAF and SSL, and lock your server so it only accepts traffic from Cloudflare, which hides your origin IP.


